TL;DR — Action required
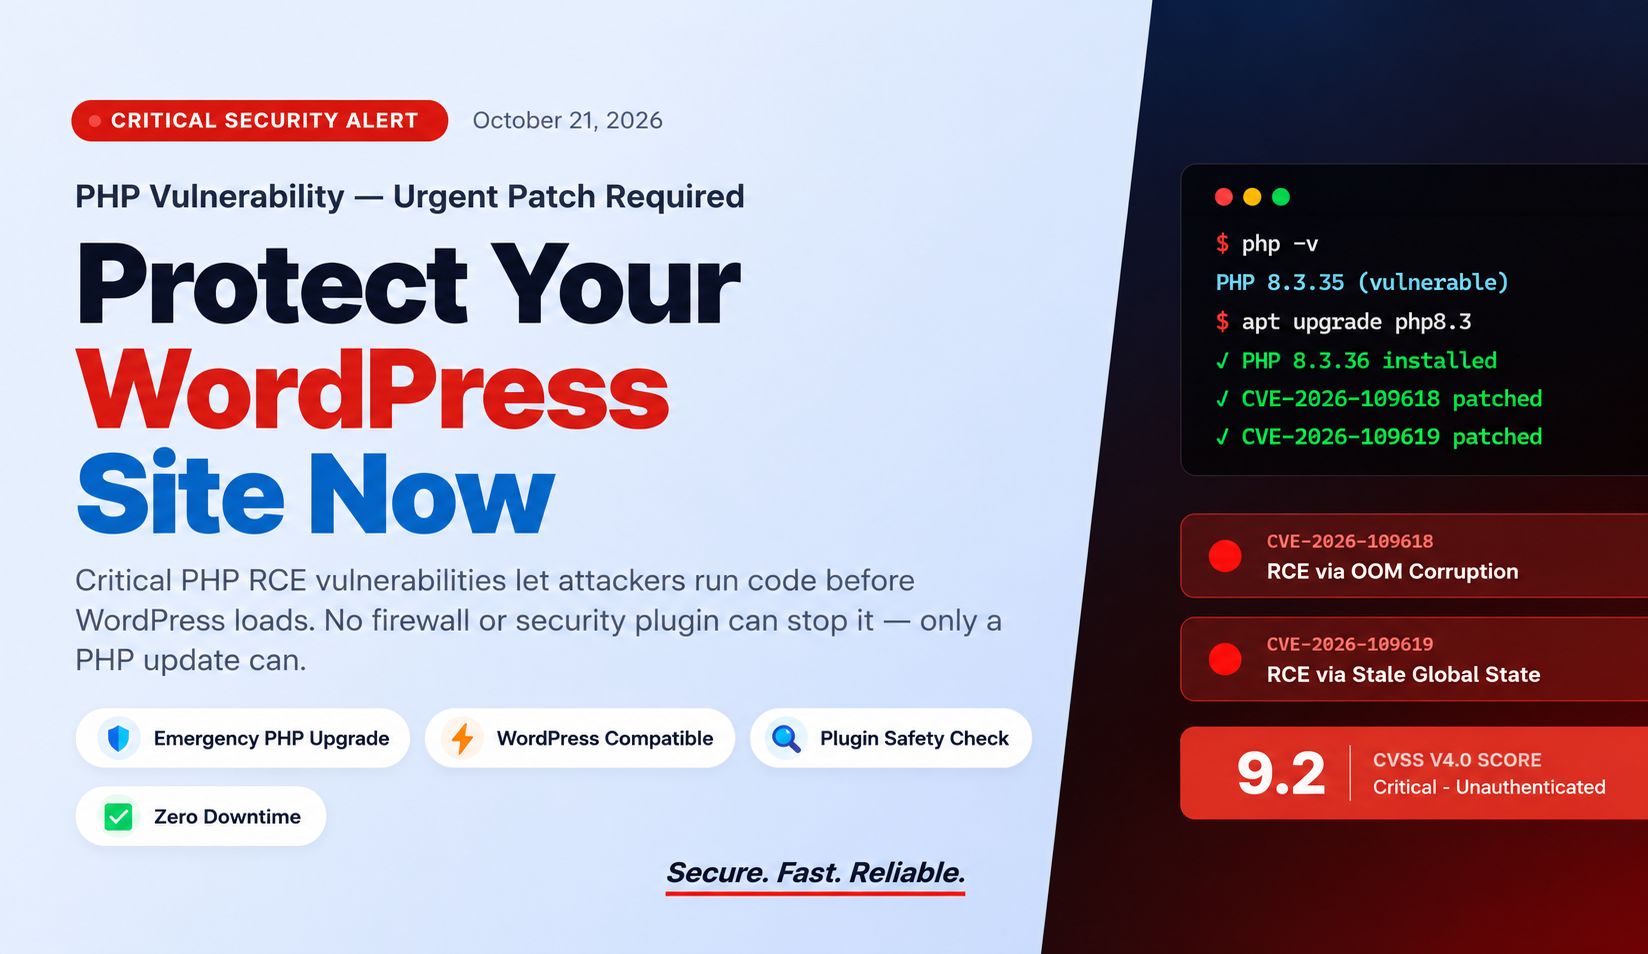
Update PHP immediately to 8.5.12, 8.4.27, 8.3.36, or 8.2.35. Two critical vulnerabilities allow an unauthenticated attacker to execute arbitrary code on your server before any application code runs. WordPress, Laravel, and every other PHP-powered site is affected. There is no complete mitigation other than patching.
What happened?
On 21 October 2026, the PHP security team released emergency patches for all supported PHP branches — 8.2, 8.3, 8.4, and 8.5 — fixing two critical vulnerabilities that can be exploited by anyone who can send an HTTP request to your server. No login, no credentials, no special knowledge required.
This PHP RCE vulnerability is among the most severe in years. If your server runs any PHP-powered site — WordPress, WooCommerce, Laravel, or custom PHP apps — you are affected.
The Two PHP Vulnerabilities Explained
RCE via Out-of-Memory Corruption (CVSS 9.2)
Out-of-memory handling can interrupt PHP while internal request data is only partially initialised. Request cleanup may then treat the invalid data as valid, allowing an attacker to trigger arbitrary code execution by crafting a request that exhausts PHP’s memory limit.
Affected setups: PHP-FPM, Apache mod_php, php-cgi, FrankenPHP, LiteSpeed.
RCE via Stale Global State (CVSS 9.2)
Request-owned internal state can survive after its backing memory has been freed. A later request handled by the same PHP worker may use that stale state before normal initialisation resets it — giving an attacker a window to inject and execute arbitrary code.
Who Is at Risk?
Every PHP installation serving web requests is affected. The PHP security team considers mod_php the highest risk, with a demonstrated exploit where an unauthenticated HTTP request triggers the attack before any application code runs.
That means your firewall rules and WordPress login page offer zero protection. Wordfence, iThemes Security, and Sucuri cannot see a request that exploits a PHP-level vulnerability — only a patched PHP version can stop it.
Affected and Fixed PHP Versions
| PHP Branch | Affected Versions | Fixed Version |
| PHP 8.5 | All < 8.5.12 | 8.5.12 |
| PHP 8.4 | All < 8.4.27 | 8.4.27 |
| PHP 8.3 | All < 8.3.36 | 8.3.36 |
| PHP 8.2 | All < 8.2.35 | 8.2.35 |
| PHP 8.1 | All versions | No official patch (end of life) |
| PHP 7.x / 8.0 | All versions | Source backport only (end of life) |
PHP 8.1 and older receive no official patches. If your site still runs PHP 7.4, 8.0, or 8.1, upgrading to PHP 8.2 or 8.3 is the only safe path. Source-level backports exist for 7.4, 8.0, and 8.1 for those compiling from source.
How to Update PHP Immediately
- Check your current PHP version. Run php -v in SSH or check your hosting control panel.
- Managed hosting (Hostinger, SiteGround, WP Engine, Kinsta): Go to your PHP version selector in the control panel and switch to the latest patched release.
- Linux VPS/dedicated: Run sudo apt update && sudo apt upgrade php* (Debian/Ubuntu) or the equivalent for your distro.
- Verify: Confirm with php -v you are now on 8.2.35, 8.3.36, 8.4.27, or 8.5.12.
- Test your WordPress site. Check that plugins, WooCommerce, and custom code still work. PHP 8.2 and 8.3 are the safest targets for most WordPress sites.
Hosting Provider Status (22 October 2026)
| Provider | Status | Action Required? |
| Hostinger | All servers auto-patched — no action needed | None |
| SiteGround | Likely patched — verify in PHP Manager | Verify version |
| WP Engine | Check WP Engine portal | Verify version |
| Kinsta | Check MyKinsta | Verify version |
| Cloudways | Self-managed — update manually in server settings | No official patch (end of life) |
| cPanel / VPS / Dedicated | Not auto-patched | Manual update |
See Hostinger Status Page for the latest on their PHP security update incident.
Temporary Mitigations (If You Cannot Update Right Now)
Updating PHP is the only complete fix. These reduce — but do not eliminate — exposure.
For CVE-2026-109618 (in php.ini or FPM pool config):
post_max_size = 8M
upload_max_filesize = 7M
For CVE-2026-109619 (in php.ini or FPM pool config — NOT via ini_set):
fatal_error_backtraces = 0 ; PHP 8.5 only
After making changes, restart all PHP workers. These are emergency stopgaps only — patch PHP as soon as possible.
Need Help Updating PHP on Your WordPress Site?
At Hopeleaf Technologies, we offer emergency PHP version upgrades for WordPress sites — including compatibility testing for plugins, themes, and WooCommerce before going live. We have handled CVE patching and PHP upgrades for WordPress clients across multiple hosting environments.